
NHS England
Strategic data-privacy and data-sharing advisory
National privacy-by-design framework · multiple national workstreams
Read the NHS England case study
NHS, Health & HealthTech
Patient data, shared care records, clinical systems and NHS procurement all depend on governance that can be evidenced. We help NHS bodies, health and care programmes and HealthTech suppliers resolve information-governance, data-sharing, clinical-safety and cyber-assurance requirements before they slow delivery or block adoption.
View Relevant Case Studies Not sure where to start? Tell us what you need to decide or resolve.
Regulatory roadmap
Choose a stage to see where we typically start. If you continue to Pathfinder or an enquiry, your selected sector and stage travel with the link. They are included with your enquiry only when you send it.
Assess stage selected: 2 relevant service pathways.
For digital health manufacturers who need DTAC evidence ready before NHS buyer review.
Explore NHS DTAC Readiness & AssuranceFor suppliers and NHS teams who need DTAC, DSPT and clinical-safety evidence that stands up to buyer and assurance review.
Explore HealthTech Governance & Clinical SafetyFor a defined clinical risk management workstream, explore clinical safety consultancy services. Applicability and scope are agreed for the product or deployment; this is not a CSO appointment.
Your chosen stage is added to the form so you don't have to repeat it. You can change anything before sending.
Relevant experience
Strategic data-privacy and data-sharing advisory
National privacy-by-design framework · multiple national workstreams
Read the NHS England case study
Three-year managed service: Information Governance, data quality, Payment by Results, trust-wide information security and clinical systems safety, reporting to the board-level SIRO
Three-year managed IG, data quality, security & clinical systems safety service · reporting to the board-level SIRO
Read the Royal Brompton & Harefield NHS Foundation Trust case study
NHS DSPT compliance and annual Information Governance support
Full DSPT compliance · commissioned annually
Read the Liverpool John Moores University case study
NHS IG Toolkit / DSPT compliance and retained advice, support and training
IG Toolkit level 2 in under two months · retained annually
Read the The Myton Hospices case study
Information Governance consultancy
NHS IG Toolkit and DSPT-aligned Information Governance
Read the CRGH case studyClient voices
“IG Smart worked alongside us to audit our practice, prepare our evidence, identify gaps and build an action plan to enable us to become level 2 compliant, which we achieved (with a lot of hard work!) in under two months.”
 David PrattDirector of Strategy & Business Development, The Myton Hospices
“One project in particular illustrates their attention to detail and concern for quality, which was the assistance and successful submission of our NHS IG Toolkit for 2015-2016.”
 Marion WilsonGeneral Manager, The Centre for Reproductive & Genetic Health
“They have developed key frameworks that have left our Information Governance processes at the Royal Brompton in a manageable state. IG Smart Ltd proved to be a safe pair of hands to partner with.”
What is at stake
Integrated care depends on lawful, proportionate data sharing between bodies with different responsibilities, systems and governance maturity.
Suppliers are asked for assurance evidence before contracts or deployment. Gaps in that evidence delay adoption regardless of product quality.
Digital health systems introduce clinical risk that has to be identified, managed and documented by the right people at the right time.
Health data is highly sensitive. Security controls need to be tested and mapped to the obligations that actually apply.
How we help
Depending on the organisation, activities and jurisdiction, relevant requirements may include:
For digital health manufacturers who need DTAC evidence ready before NHS buyer review.
Manufacture and deployment/use responsibilities remain distinct.
DTAC support is preparation/internal review where agreed, not NHS approval or certification, and not independent assurance over IG-Smart’s own delivery. Manufacturer and NHS-buyer responsibilities remain distinct.
Working with us
Assessment, audit, readiness, remediation, assurance and defined programmes.
Ongoing specialist governance and assurance where continuity matters.
Multi-framework, cross-functional, multi-jurisdictional or enterprise requirements.
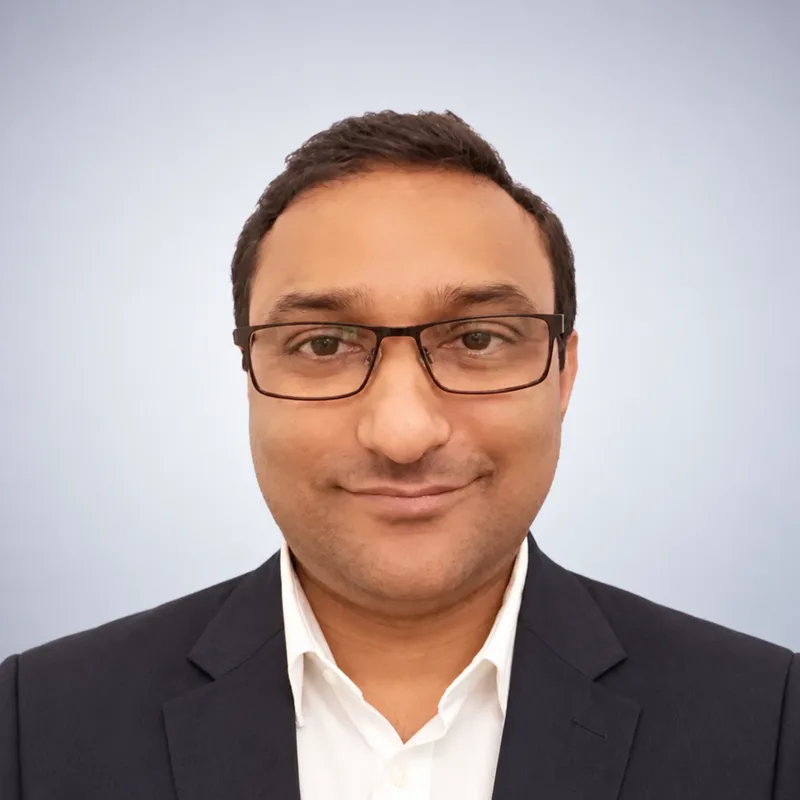
Himanshu Desai
Strategic Health Informatics Leader & Clinical Safety Officer
Combines experience in pharmacy and health informatics with completed Digital Clinical Safety – Practitioner training, and extensive experience across NHS, healthcare technology, clinical applications and international health systems.
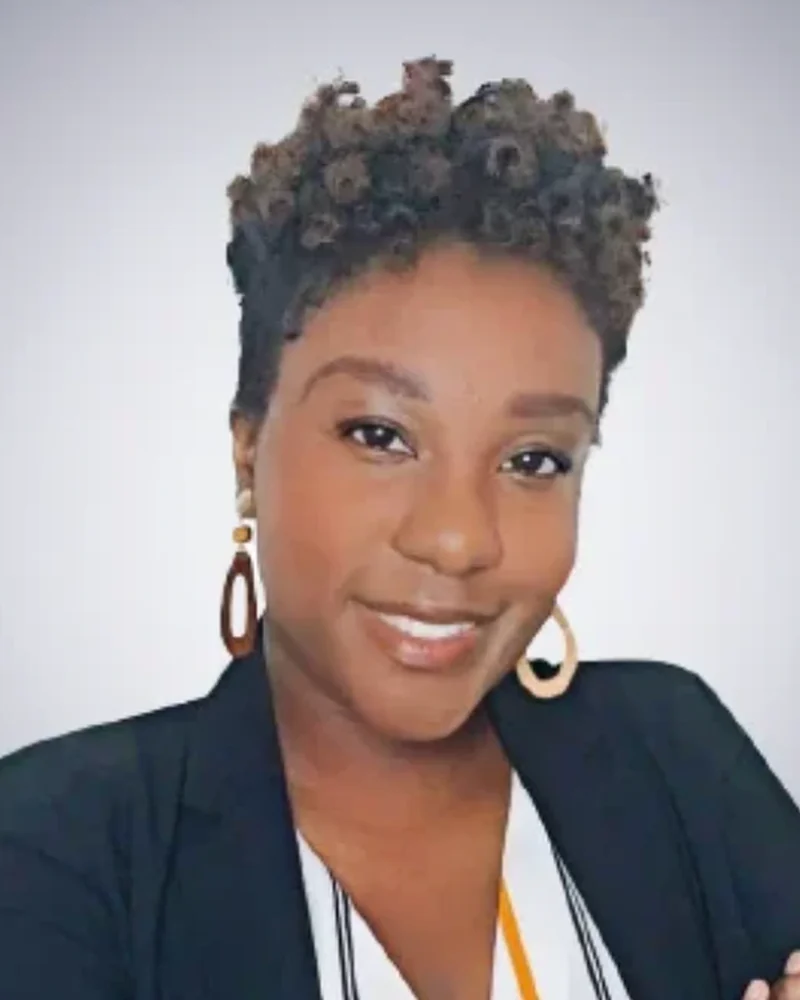
Shaista Peart
Senior Privacy & Digital Compliance Consultant
Privacy and information governance specialist advising organisations on data protection, DPO responsibilities and practical governance across healthcare and regulated environments.
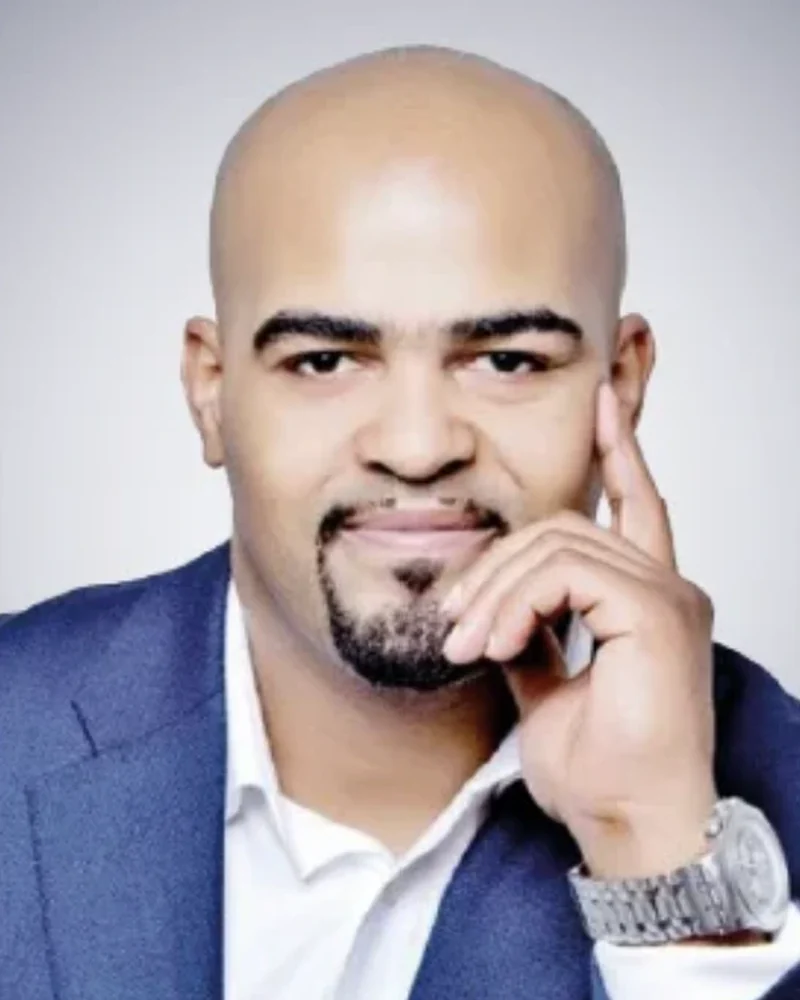
Michael Abtar
CEO and Founder
Governance, risk and assurance specialist with more than 18 years' experience spanning privacy, cyber resilience, AI governance, digital transformation, healthcare and complex regulated organisations.
For procurement teams:Engagement modelsTrust CentreRequest relevant evidence
Tell us what you need to decide or resolve, or share a defined requirement for review.