Data Privacy & Information Governance
Managed Data Privacy Programme
- Processing change
- Risk / DPIA
- Decision
- Action
- Oversight
- Reporting
18+ yearsSenior practitioner experience
150+ jurisdictionsSupporting clients whose operations span them
Global audit deliveryInternational assurance and audit experience
ISO/IEC 27001:2022Certified information-security management
Ongoing privacy governance, not one-off advice — with defined-scope assessment or remediation available where a baseline needs to be established first.
Senior-led by Michael Abtar, CEO and Founder · LLB (Hons), PG.Dip.Law, Cert. DPO
When organisations engage us
Signals that it is time to act
- Privacy obligations are growing faster than in-house capacity
- DPIAs, rights requests and incidents are handled inconsistently
- The board needs regular, evidenced privacy reporting
- A DPO is in place but the wider privacy programme has no owner
- Multiple entities, jurisdictions or suppliers complicate compliance
- Audit, procurement or regulator scrutiny is approaching
What the service covers
Outcomes the service is built to deliver
- Governance and accountability
- A clear privacy governance structure, defined roles and a documented accountability framework.
- Policy and control framework
- Support to maintain policies, notices and controls as processing and regulation change.
- Processing governance
- Oversight of records of processing and how new or changed processing is assessed.
- DPIA, risk and issue governance
- Structured handling of DPIAs, privacy risks and issues, with clear escalation.
- Rights, incident and escalation governance
- Defined routes for rights requests, personal-data incidents and decisions that need senior attention.
- Executive, board and regulator-ready reporting
- Regular reporting that gives leadership an evidenced view of privacy risk and progress.
- Prioritised improvement planning
- A risk-based roadmap so effort goes where it reduces most exposure.
- Ongoing senior advisory support
- Access to senior practitioner judgement as questions arise.
How we deliver
Assess → Build → Manage → Assure → Improve
Assess
Baseline current privacy governance, risk and evidence.
Build
Agree the governance model, priorities and reporting rhythm.
Manage
Run the programme: oversight, advice, issue and risk governance.
Assure
Evidence progress for leadership, auditors and regulators.
Improve
Refresh priorities as processing, risk and regulation change.
Scope boundaries
Included, and separately scoped where required
Included in the core service
- Governance, oversight and structured programme management
- Senior advice and independent challenge
- Risk-based prioritisation
- Management and board reporting
Separately scoped where required
- Operational administration at scale
- Extensive remediation delivery
- Large implementation programmes
- Specialist cyber, legal or international-transfer deep dives
- Resource-heavy privacy-office execution
What you receive
Outputs you can picture before you engage
Illustrative structure — not a client document
Example content shown for illustration only.
Privacy decision register
| Ref | Decision | Rationale | Owner | Status |
|---|---|---|---|---|
| D-01 | Approve new analytics processing | DPIA complete; residual risk accepted | Head of Product | Closed |
| D-02 | Extend retention for support records | Legal basis reviewed | Operations lead | Open |
| D-03 | New international supplier | Transfer assessment pending | Procurement | Escalated |
Relevant evidence
Relevant evidence
 View the evidence: accuRx
Named client · Healthcare / NHS
accuRx
Retained DPO and NHS IG support
Retained DPO services · privacy and NHS information-governance support during growth
 View the evidence: Banham Group
Named client · Security Services & Technology
Banham Group
Defined-scope assessment → retained managed DPO service
Gap analysis → implementation support → outsourced DPO since 2020
 View the evidence: Glenmark Pharmaceuticals
Named client · Life Sciences / Pharmaceutical
Glenmark Pharmaceuticals
Retained external DPO service
Retained external DPO · EU & LATAM remit
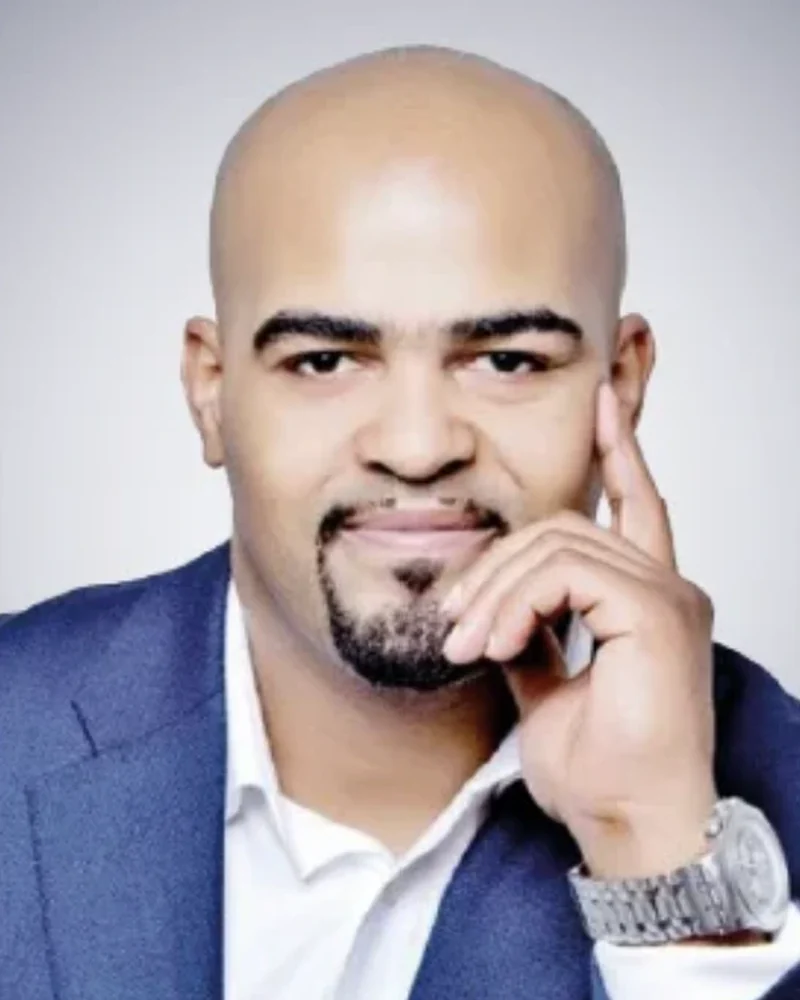
Service lead
Michael Abtar · CEO and Founder
LLB (Hons), PG.Dip.Law, Cert. DPO
Governance, risk and assurance specialist with more than 18 years' experience spanning privacy, cyber resilience, AI governance, digital transformation, healthcare and complex regulated organisations.
Experience includes governance and assurance work involving more than 100 million consumer records.
View profileInvestment
Scoped to requirement
Delivered as a managed & retained service. Scope, deliverables, assumptions and fees are agreed in writing before work begins.
Talk to a Senior Practitioner How engagements & investment work
Fees reflect factors such as
- Organisational scale and complexity
- Number of entities and jurisdictions
- Scope of retained responsibility
- Existing maturity
- Volume of remediation support
- Required availability
- Assurance and reporting requirements
Questions
Frequently asked questions
Is this the same as an outsourced DPO?
No. A DPO provides independent oversight of compliance. This programme provides structured, ongoing privacy governance capability. It can run alongside a DPO — internal, or provided by IG-Smart — with decision rights kept clearly separated.
Do we need to appoint IG-Smart as our DPO?
No. The programme can operate with or without a formal DPO appointment. Where a designated DPO is also required, see our Outsourced & Fractional DPO Services.
Can it work alongside our internal privacy team?
Yes. Scope is agreed around the capability you already have, so the programme strengthens your team rather than duplicating it.
What is not included?
Operational administration at scale, extensive remediation, large implementation programmes and specialist deep dives are scoped separately where required, so the core programme stays focused on governance, oversight and reporting.
Next step